Security your regulator can read
We name the control, show where it lives and give your auditors the evidence. No vague badges — just how BankQore protects your money and your data.
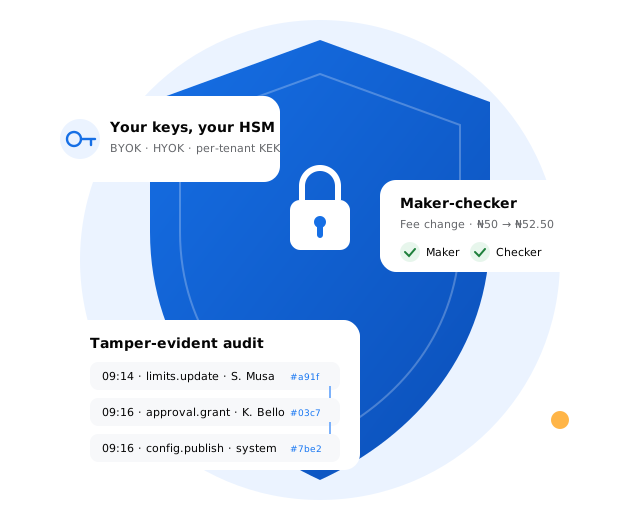
Built into the platform, not added later
Keys you control
Per-tenant key-encryption keys in cloud KMS or FIPS 140-3 Level 3 HSMs. Bring your own key on Growth, hold your own on Sovereign.
Maker-checker everywhere
Configuration, limits, roles and sensitive money movement need a second person. Nobody approves their own change.
Tamper-evident audit
Hash-chained audit, session and communication logs, streamed live to your compliance team and your SIEM.
Strong identity
MFA and passkeys for staff and customers, staff SSO with Entra ID or Okta, step-up for risky actions.
Card data isolated
Card numbers live in a separate card vault with its own PCI scope; our web apps never see them.
Hardened runtime
Restricted pod security, service mesh with mutual TLS, strict CSP and tokens kept on the server.
Where we stand, honestly
Our controls are mapped to these frameworks today. Formal certifications are on the roadmap; we'll update this table as each audit completes.
| Framework | Status | Notes |
|---|---|---|
| CBN Risk-Based Cybersecurity Framework | Controls mapped | Evidence pack available on request |
| NDPA 2023 / GDPR | Controls mapped | Data subject requests built into customer apps |
| ISO/IEC 27001:2022 | Planned | Certification targeted for 2028 |
| SOC 2 Type II | Planned | Audit targeted for 2028 |
| PCI DSS v4.0.1 | Planned | Level 1 targeted; card vault designed as a separate scope |
Found a vulnerability?
We welcome responsible disclosure and reply within two business days.
Bring your CISO to the demo
We'll walk through architecture, keys and audit with your security team.